Skip to content Skip to footer
SIEM / XDR

Wazuh
Open-source platform with SIEM and XDR capabilities

We are an official Wazuh partner in Argentina: reliable and scalable SIEM solutions.

Typical operational risks in infrastructure without SIEM/XDR

No centralized view of security events (logs)
Critic
Endpoints without integrity monitoring (FIM) or change detection
Critic
Noisy alerts: many false positives and no prioritization
Risk
No security hardening/benchmarking (SCA) or security configuration management
Risk
Vulnerabilities that are not being tracked or prioritized for remediation
Critic
Incident response without automation (block/active response)
Room for improvement
wazuh
About Wazuh

What is Wazuh?

Wazuh is an open-source platform designed for threat detection, security monitoring, incident response, and regulatory compliance.

End-to-end security

Monitor, detect, and respond to incidents in real time with a platform designed to protect your physical, virtual, and cloud infrastructure.

Fast and efficient implementation

As an official partner, we have proven expertise in seamlessly integrating Wazuh into your IT environment without disrupting your operations.

Specialized support

Our cybersecurity team is with you every step of the way: from initial setup to ongoing maintenance and updates.

Comprehensive Wazuh services for your business

Wazuh

Key capabilities and features

Explore each module:

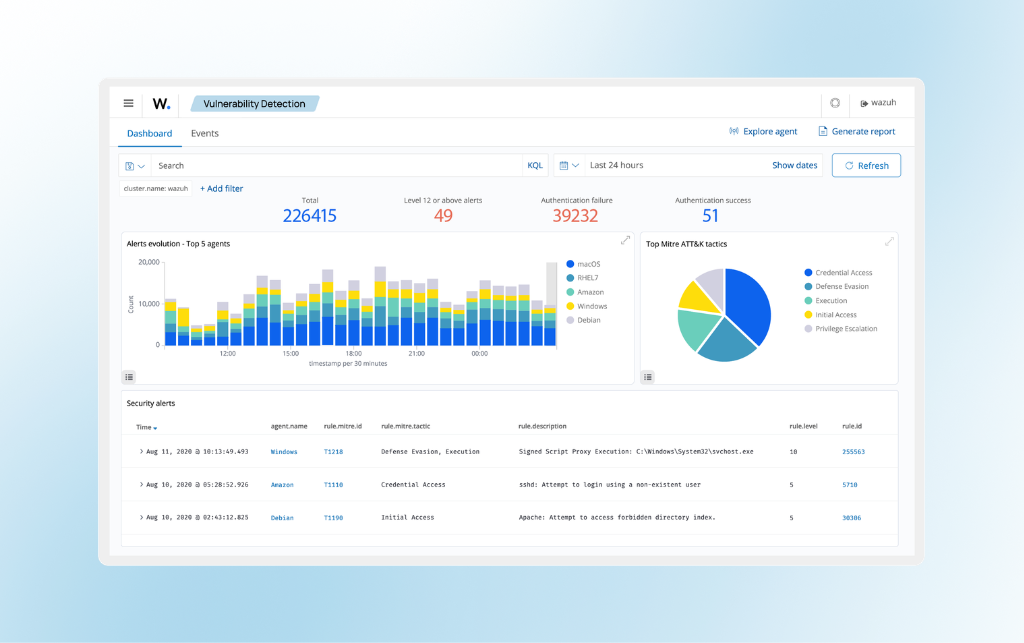
Security log analysis

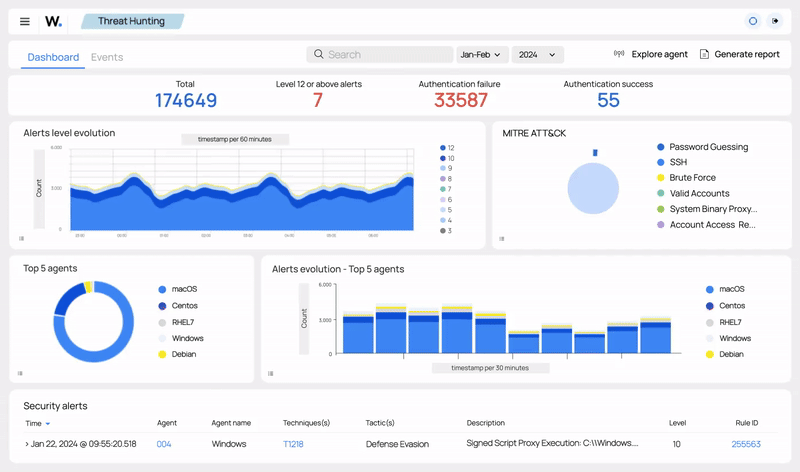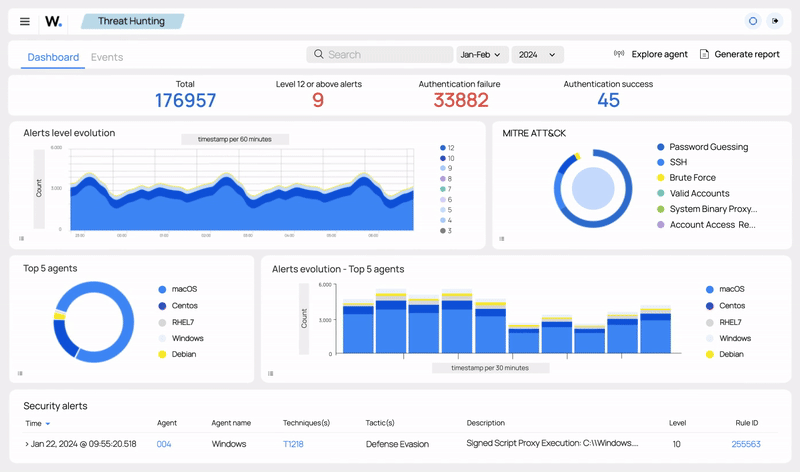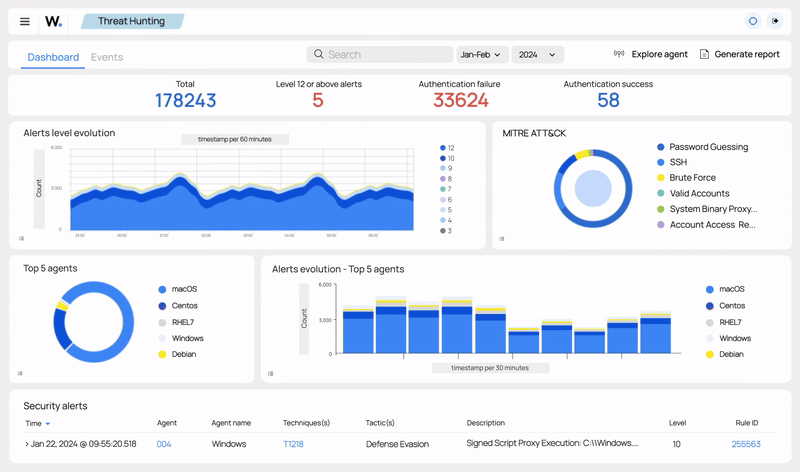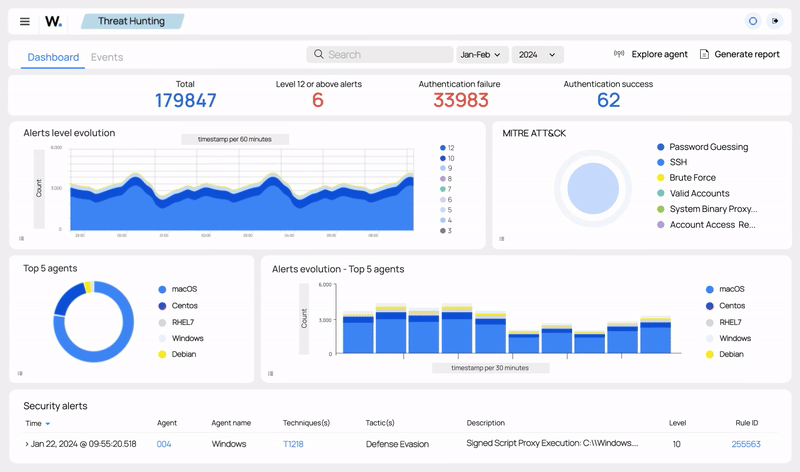
Protect your infrastructure and streamline compliance by monitoring and auditing endpoint activity. Wazuh aggregates, stores, and analyzes events to detect anomalies and indicators of compromise. Add context to alerts to speed up investigations and reduce response times.

  • Centralization of events and auditing.
  • Anomaly detection and IOCs.
  • Context-rich alerts for faster investigations.
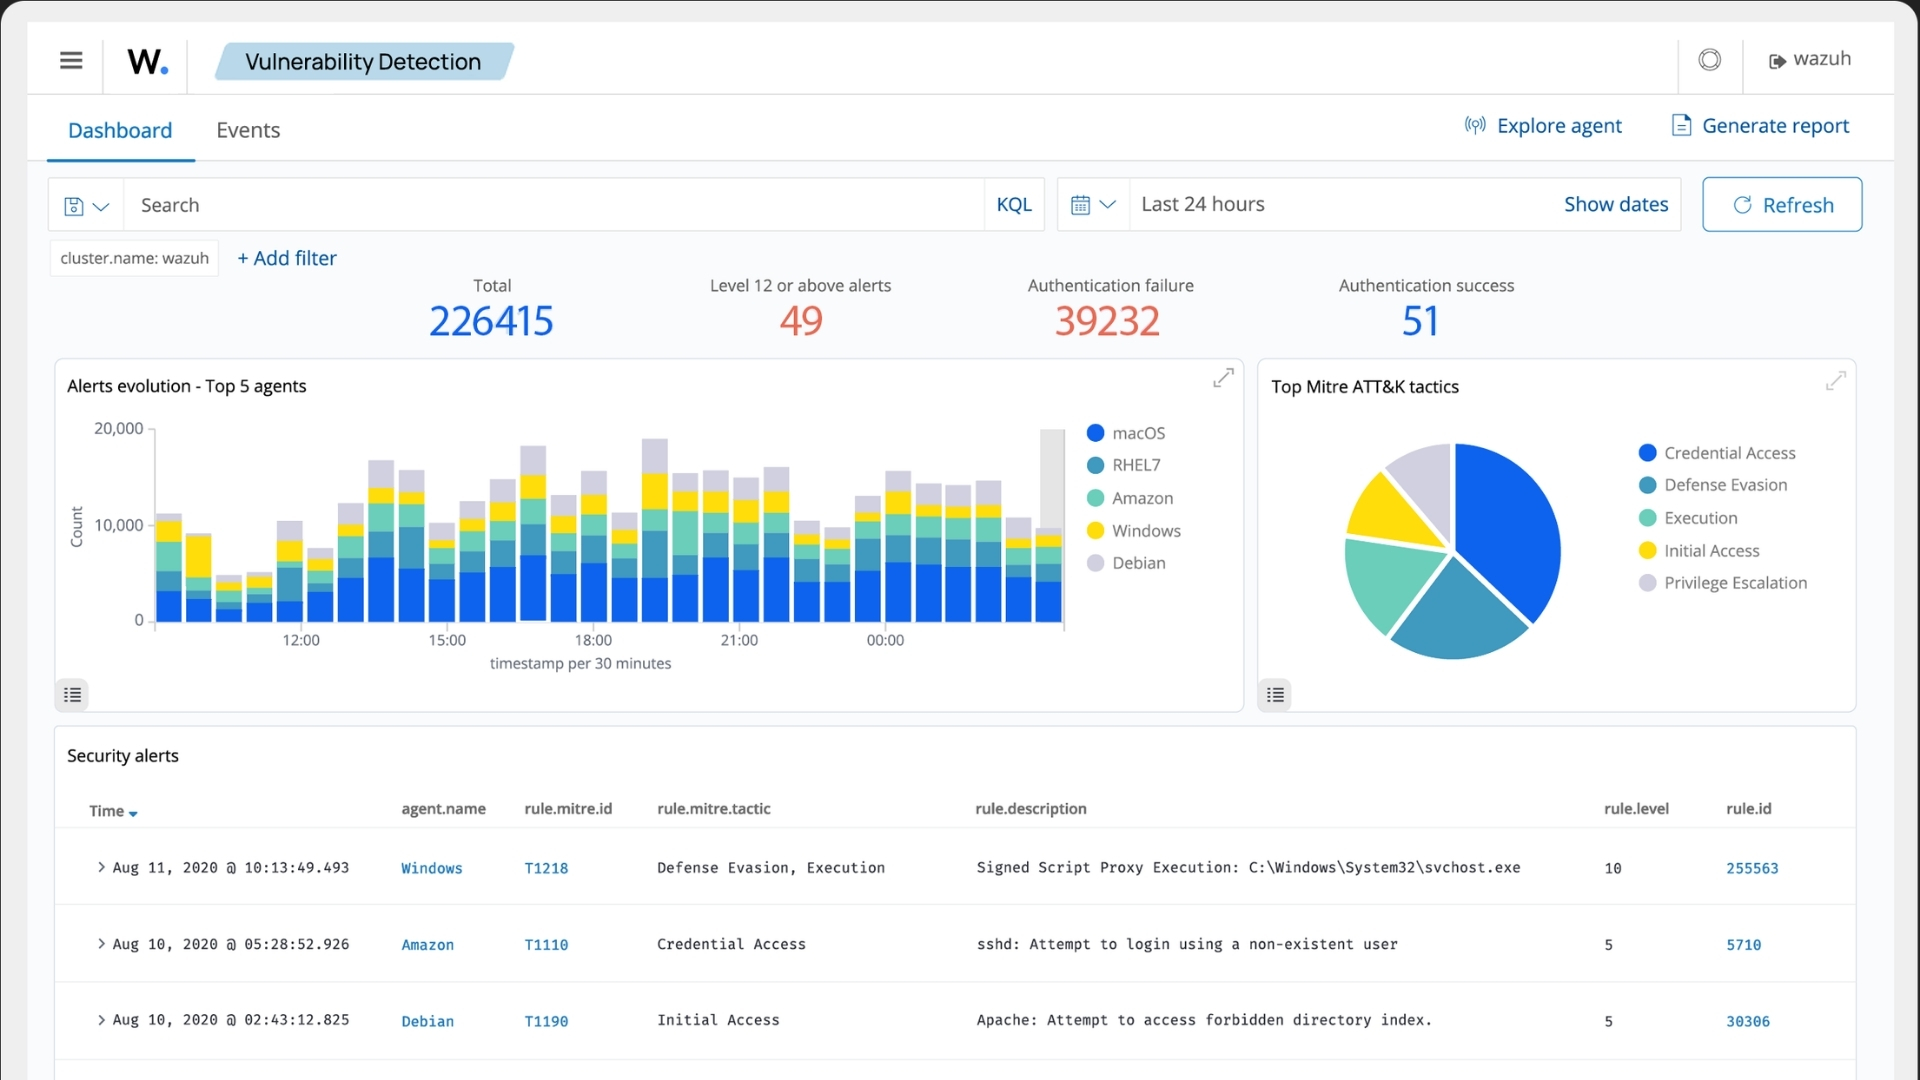
Vulnerability detection

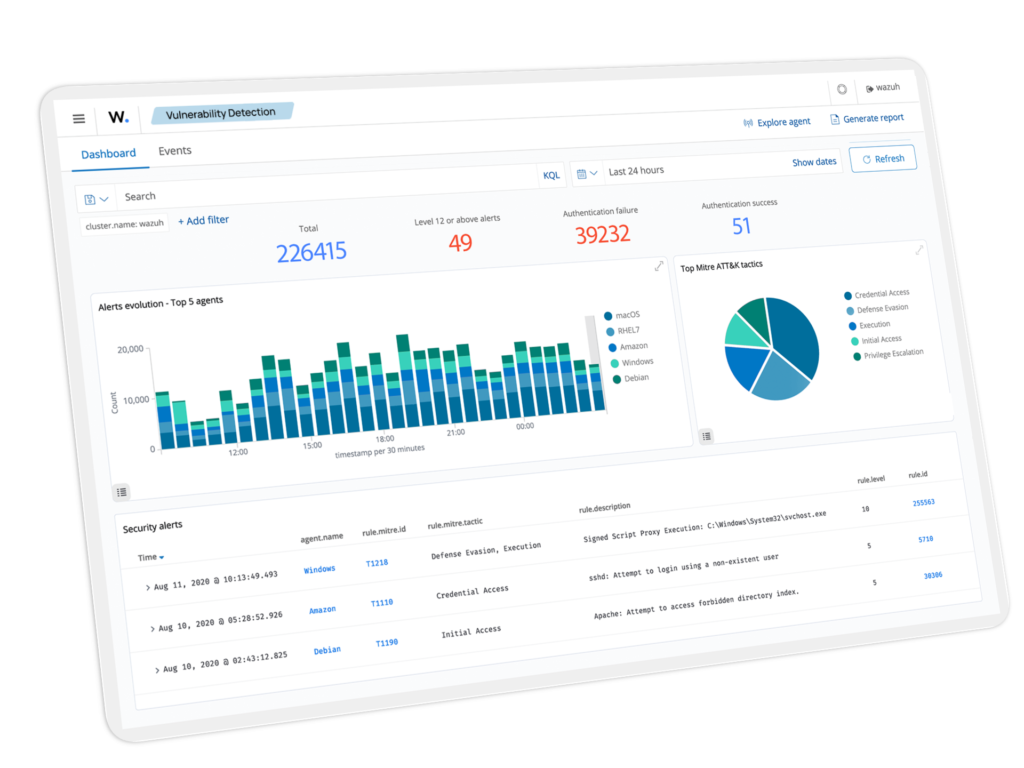
Detect vulnerabilities on endpoints where you have deployed the Wazuh agent. Prioritize findings to speed up decision-making and remediation, reducing the attack surface and compliance friction.

  • Continuous identification of CVEs.
  • Prioritization for targeted remediation.
  • Improved safety posture.

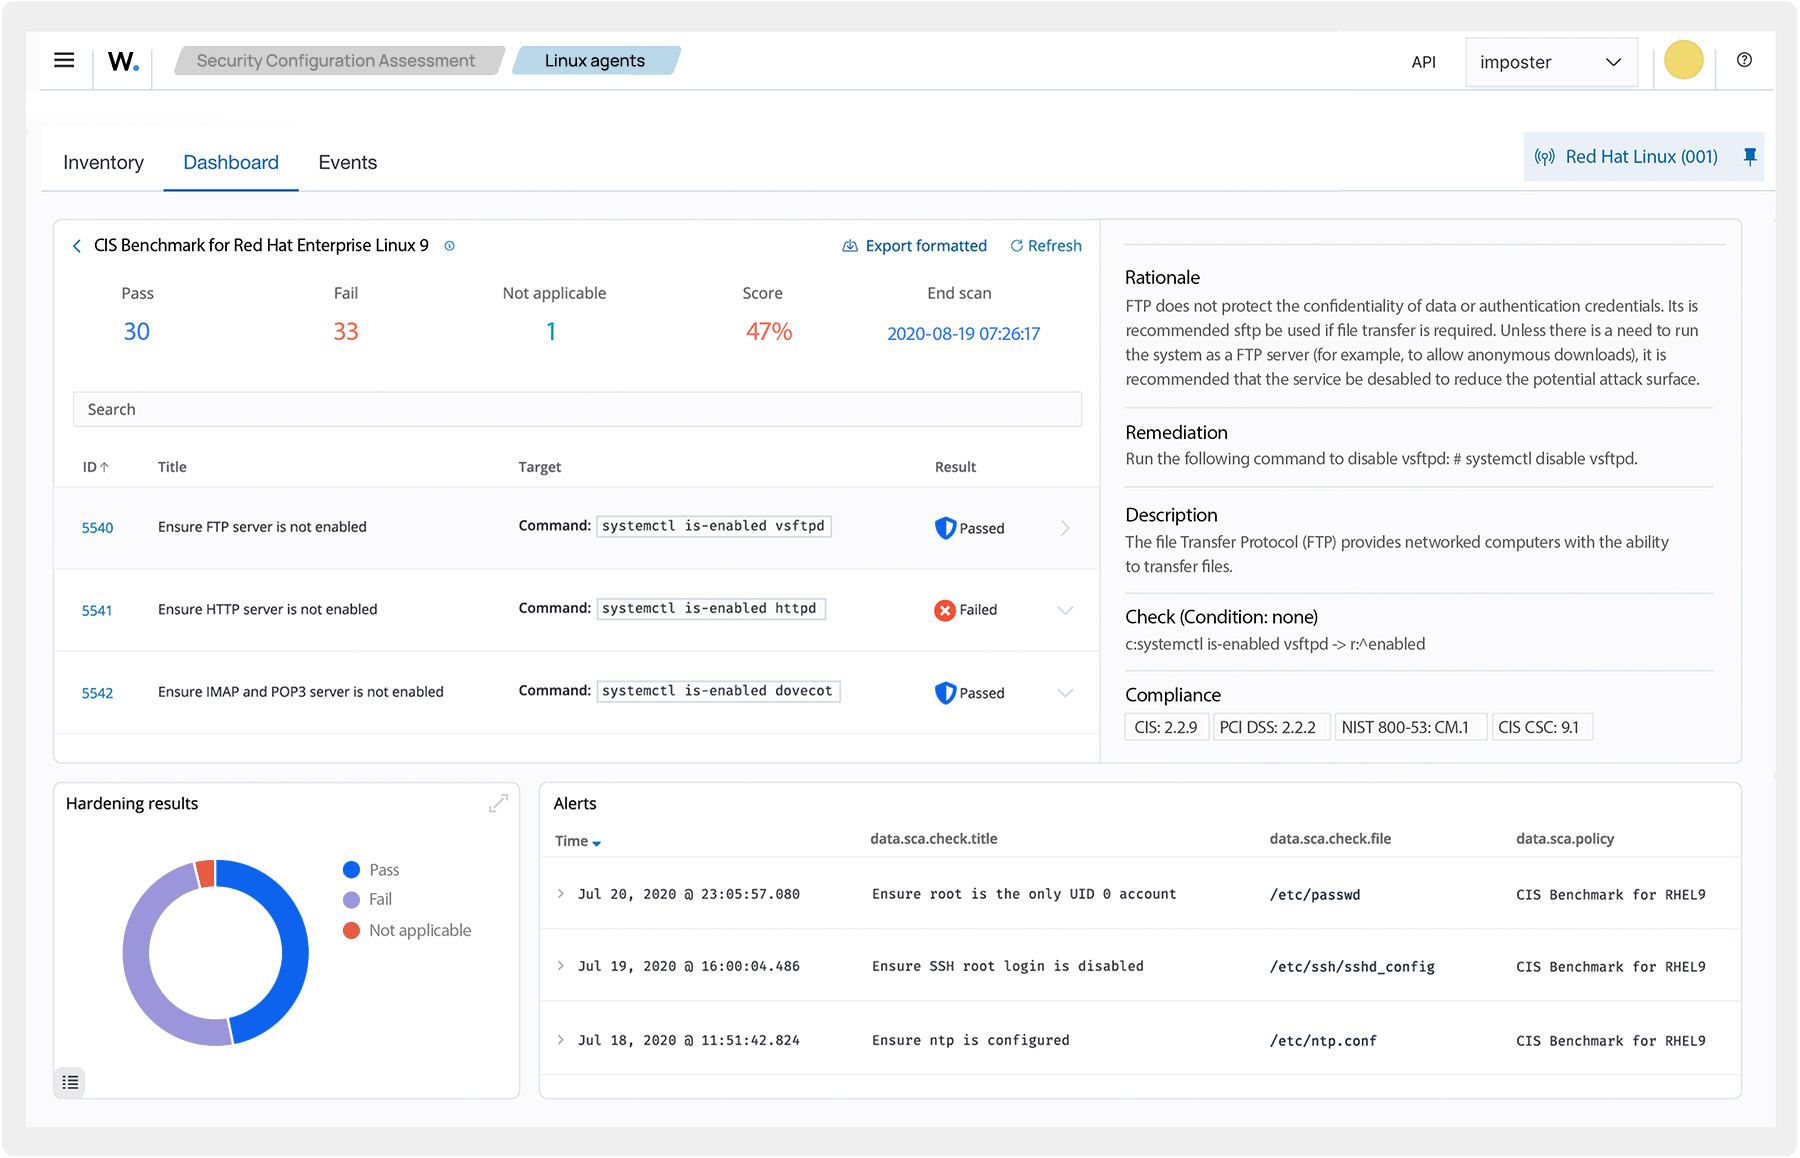
Configuration Assessment (SCA)

Identify misconfigurations and security vulnerabilities. Wazuh scans systems against benchmarks (e.g., CIS) to detect deviations from best practices and standards.

  • Benchmark comparisons (e.g., CIS).
  • Identification of misconfigurations and gaps.
  • Foundation for hardening and auditing.

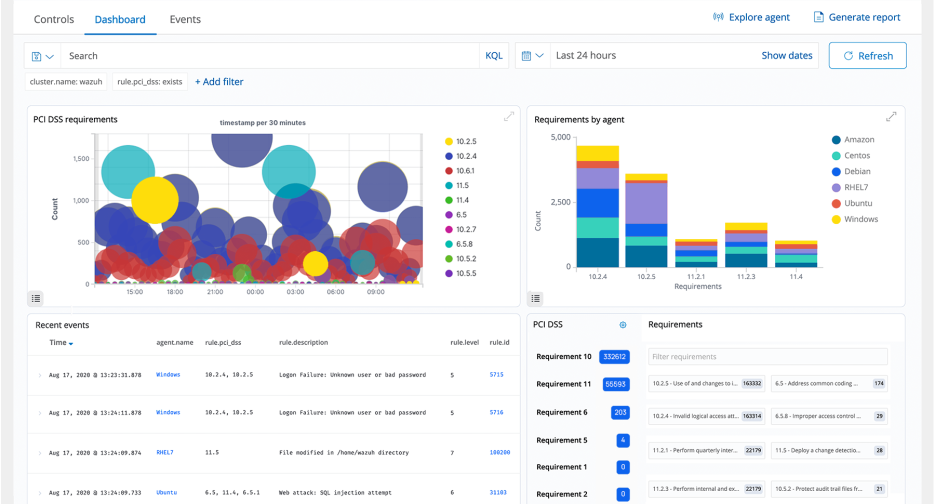
Regulatory Compliance

Simplify compliance with evidence, traceability, and reporting. Wazuh helps demonstrate compliance with frameworks such as PCI DSS, NIST 800-53, GDPR, SOC 2, and HIPAA.

  • Support for multiple regulatory frameworks.
  • Audit evidence.
  • Less operational friction in compliance.

Alerts and notifications

Real-time alerts when incidents occur. Event correlation, integration with threat intelligence, and customizable dashboards and reports. You can adjust rules and thresholds to suit your operations for a rapid response.

  • Real-time alerts and correlation.
  • Threat intelligence and integrations.
  • Customizable notifications.

SIEM Event Reporting and Insights

Actionable reports for monitoring, documentation, and continuous improvement. Ideal for technical teams and audits: metrics, trends, and findings, tailored to your needs.

  • Executive and technical reports.
  • Insights for prioritization.
  • Evidence for compliance.
Wazuh Partner

Official partner in Argentina

Fostering success

Centralized and h
security true threat detection

We are an official Zabbix partner in Argentina, providing consulting, technical support, and IT monitoring solutions to companies across the country. If you're looking for Zabbix experts in Argentina, CTL has the team you need.

Implementation with a focus on real-world security

We don't just install the platform. We design the architecture, configure detection rules, define relevant alerts, and tailor Wazuh to each organization's risks and needs.

Continuous operation and optimization

We support daily operations by fine-tuning rules, reducing false positives, and improving visibility to ensure efficient and reliable detection.

Integration and Evolution of the Ecosystem

We integrate Wazuh with existing tools and support the evolution of the security strategy, aligning the platform with business objectives.

wazuh

The strength of an official partner in IT security

2740 Patagones St., Technology District, Buenos Aires
+54 9 11 2291-6311
Questions

Questions Frequently Asked Questions

We don’t just sell the tool. At CTL, we implement, configure, operate, and support Wazuh from start to finish. Design, deployment, tuning, alerts, dashboards, and ongoing support. You identify risks. We manage them.

For both. Wazuh is used for incident detection as well as for audits and compliance (ISO 27001, PCI DSS, GDPR, etc.). Security and compliance on a single dashboard. Less noise, more control.

Physical and virtual servers, cloud, containers, endpoints, firewalls, switches, critical applications and services. On-premises, cloud, or hybrid. If it runs in your environment, it can be monitored.

In many cases, yes. Especially if you're looking to cut costs without sacrificing visibility. Wazuh supports SIEM, XDR, and FIM use cases. Plus, it's open-source, with no per-event licensing.

The difference lies in how it works. Wazuh, without customization, generates a lot of noise. CTL tailors it to your business, determines what matters and what doesn't, sets up actionable alerts, and supports you with a team that knows exactly where to look when something goes wrong.

Blog

Learn more about Wazuh

Ready to take the
next step?

Complete the form and schedule a personalized meeting with one of our experts.

Loading Form